Thursday's AI sell-off was not about demand. It was about who pays. The Nasdaq fell 2.6 per cent, Meta unveiled non-voting shares to fund its build-out and Nvidia's Jensen Huang warned of a scarcity of capital, as OpenAI raced to close up to $30 billion at $1.25 trillion. Retracement or reckoning?
SpaceX posted a US$4.4 billion quarterly profit as AI revenue surged, while Tesla and SpaceX courted Korean suppliers for their Terafab chip project in Texas. Musk is targeting production in 2028 as the companies also explore a potential merger.
ServiceNow’s AI Passport aims to govern what enterprise AI agents can do, using signed credentials and runtime checks. With NVIDIA supporting enforcement, the test is whether permissions can be upheld and revoked across third-party systems as businesses move agents into production safely at scale.
Digital Dystopia: How Asia-Pacific Became Cybercrime's Promised Land
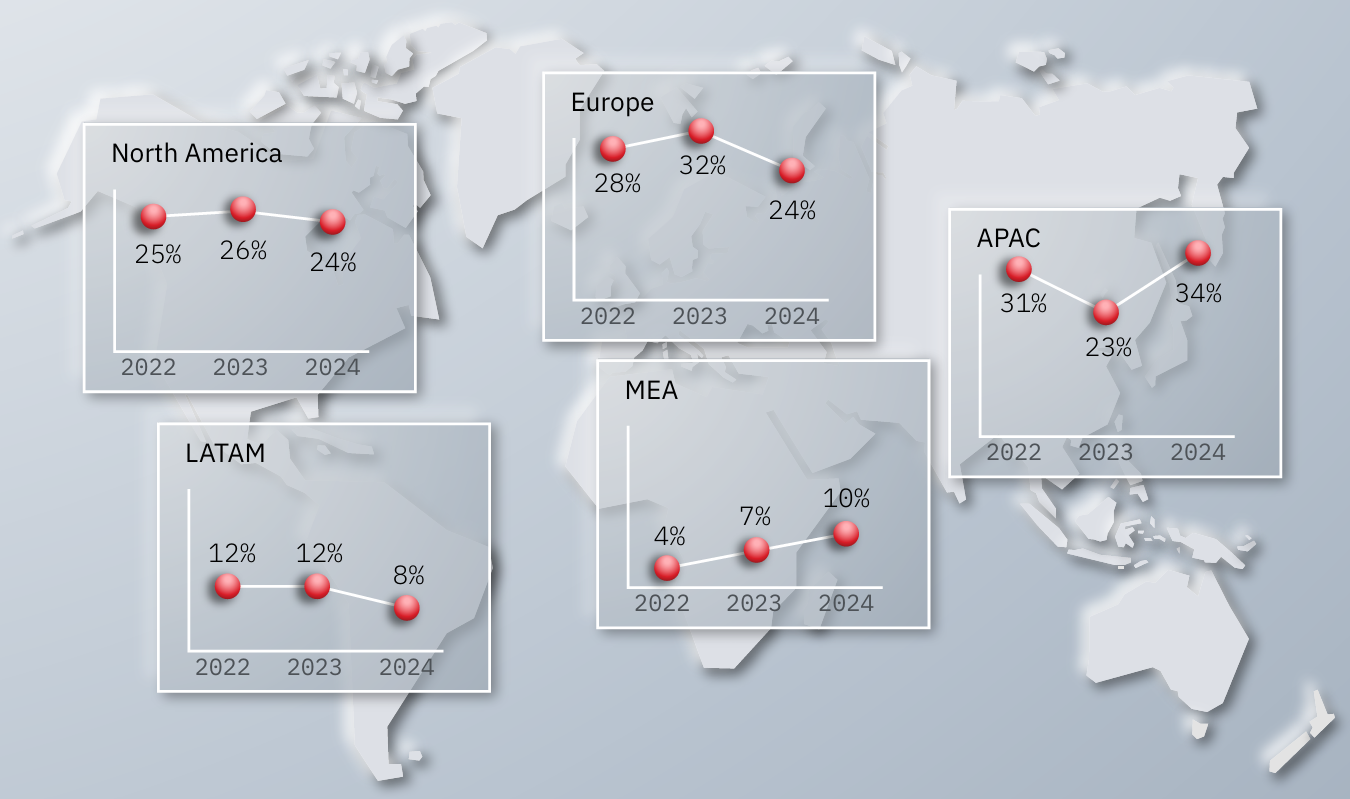
Asia-Pacific faced over one-third of all cyberattacks in 2024, making it the world’s top target. From manufacturing breaches to talent shortages and rising ransomware, CNC investigates how a region of digital ambition became cybercrime’s global epicentre.
Across the sprawling digital archipelago of Asia-Pacific, a perfect storm of vulnerability and opportunity has created the world's most lucrative hunting ground for cybercriminals. An investigation by the CNC Cyber Team reveals how a toxic combination of rapid digitalization, chronic talent shortages, and regulatory fragmentation has transformed the region into ground zero for global cyber warfare.
The evidence is stark and unforgiving. IBM'sX-Force Threat Intelligence Index 2025, released in May, confirms that Asia-Pacific absorbed more than one-third of all global cyberattacks in 2024—a concentration of digital violence that dwarfs any other region. But behind these statistics lies a more troubling narrative: the systematic exploitation of a region caught between technological ambition and security reality.
Incident response cases by geographic region
Source: IBM X-Force.
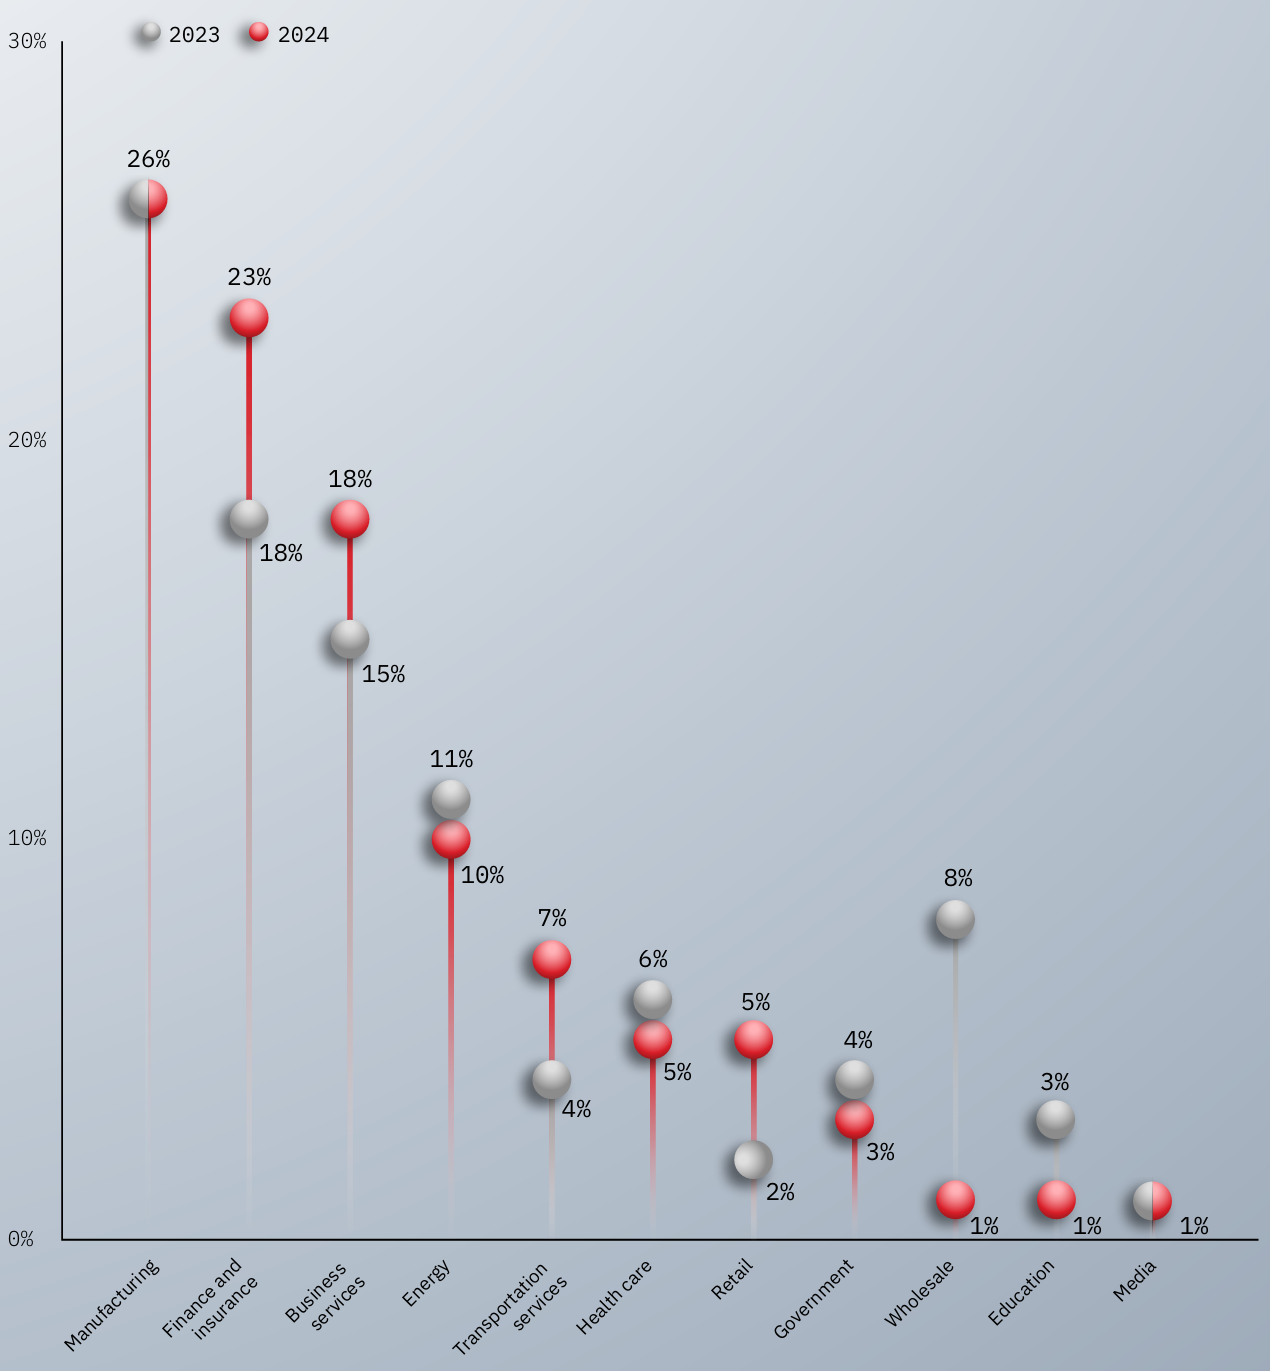
Manufacturing industries, the backbone of Asia's economic miracle, have become primary targets, accounting for 26% of regional cyber incidents. This deliberate focus on supply chains reveals cybercriminals' sophisticated understanding of global commerce vulnerabilities. Financial services follow at 23%, creating a dual assault on both production and capital flows that threatens regional economic stability.
Share of attacks by industry, 2023-2024
Proportion of incident response cases observed by X-Force for the period 2023-2024. Source: IBM X-Force.
Verizon's 2025 Data Breach Investigations Report exposes an even more disturbing evolution. System intrusions now dominate 80% of Asia-Pacific breaches—a dramatic surge from 38% the previous year. This shift signals cybercriminals' abandonment of opportunistic attacks in favor of persistent, methodical campaigns designed to establish permanent footholds within target networks.
The human cost of this digital siege becomes apparent in the daily statistics. Adrian Hia, Managing Director for Asia Pacific at Kaspersky, quantifies the relentless pressure:
"On a daily basis, we are looking at more than 145,000 attempts to break enterprises and SMBs' passwords and encryptions in Southeast Asia. That's a lot given the current shortage of cybersecurity staff in the region."
This talent crisis represents perhaps the most critical vulnerability facing the region. Malaysia's new Cybersecurity Act, despite legislative ambitions, remains hamstrung by an 84% organizational struggle to find certified cybersecurity professionals. Meanwhile, Brunei lacks basic mandates for financial sector protections, creating regulatory gaps that cybercriminals exploit with impunity.
The digital divide compounds these challenges exponentially. Nearly one-third of Asia-Pacific's population remains offline, creating a two-tier security ecosystem where connected populations face sophisticated threats while disconnected communities remain vulnerable to different forms of digital exploitation. This fragmentation prevents the coordinated response necessary to combat transnational cyber threats.
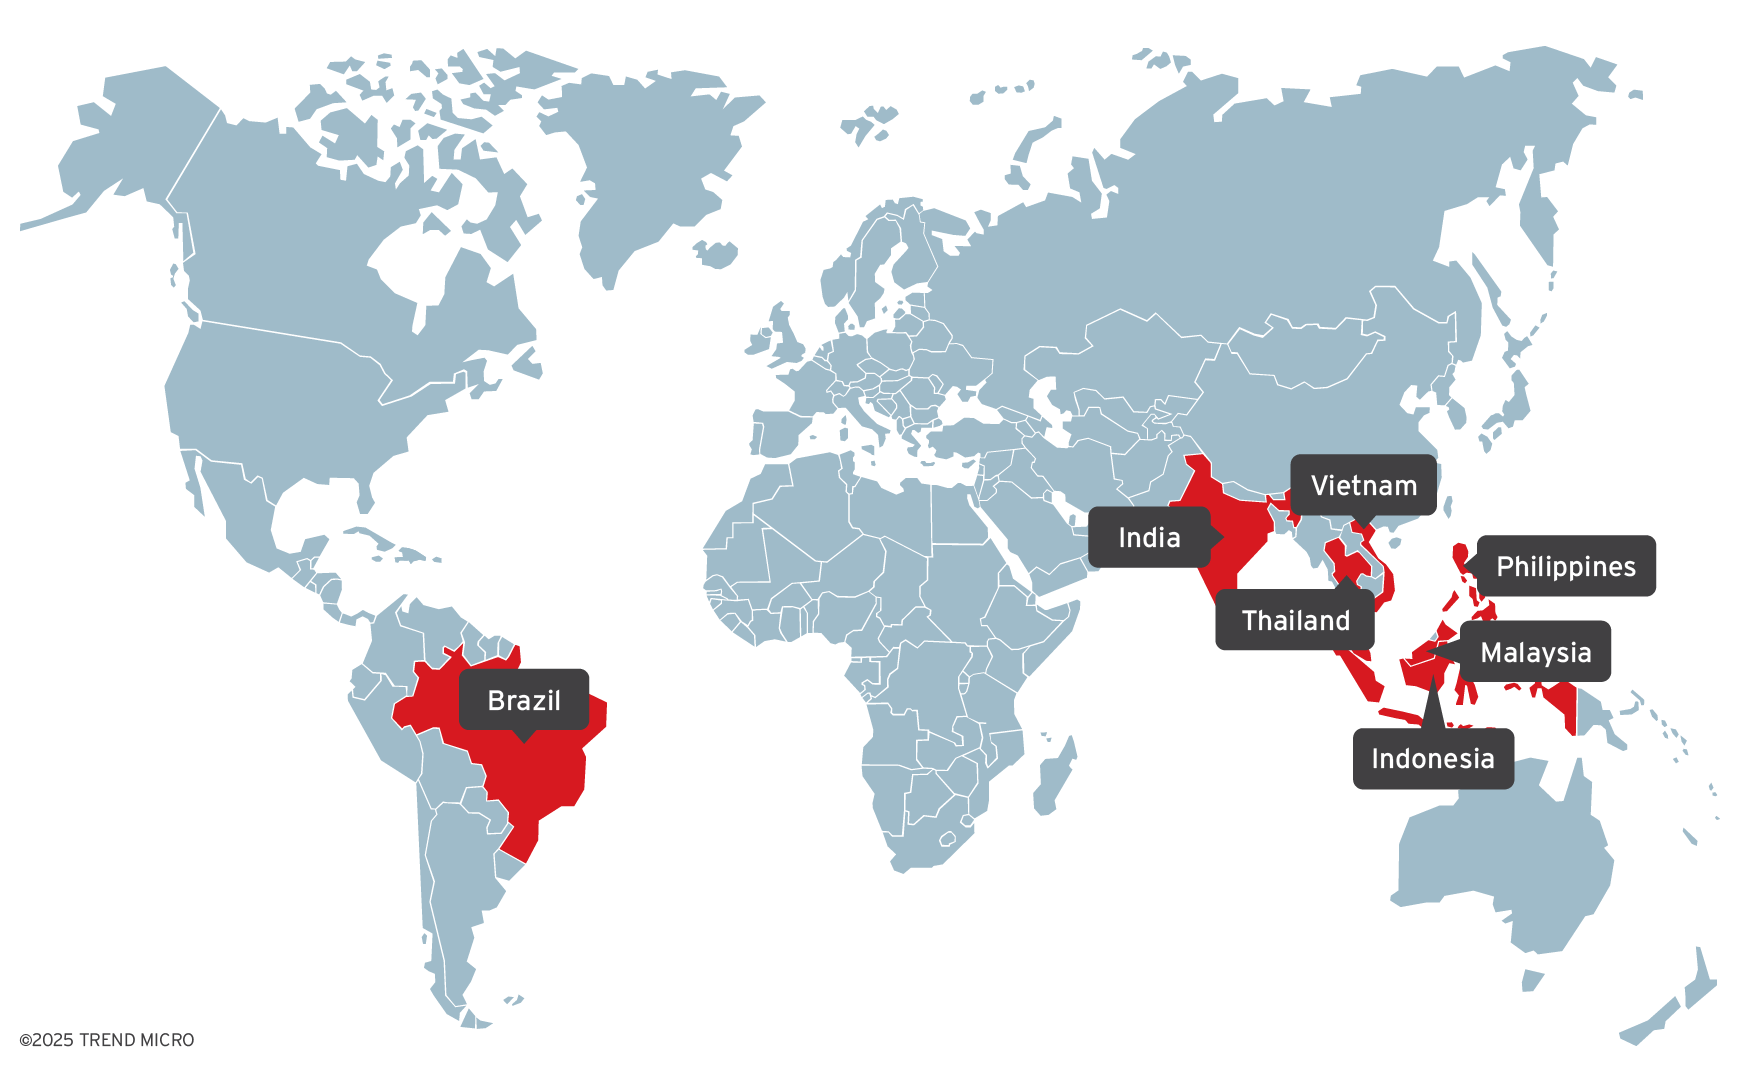
State-sponsored actors have recognized and exploited these structural weaknesses. Trend Micro's identification of "Earth Lamia," a China-linked threat group exploiting SAP NetWeaver and SQL Server vulnerabilities across Brazil, India, and Southeast Asia since 2023, demonstrates how nation-state resources amplify regional vulnerabilities. These groups operate with patience and precision, treating cybersecurity as asymmetric warfare rather than criminal opportunism.
The Coalition for Cybersecurity in Asia-Pacific (CCAPAC) has documented over 57,000 ransomware incidents in just the first half of 2024, with Indonesia, the Philippines, and Thailand bearing the heaviest assault. Attackers increasingly employ double and triple extortion tactics, transforming data theft into sustained psychological warfare that can cripple organizations for months.
As the region prepares to host over 14 billion IoT devices by 2025, the attack surface expands exponentially. Each connected device represents a potential entry point for adversaries who have already demonstrated their ability to exploit regional digital dependencies with devastating effectiveness.
Yet amid this digital chaos, a beacon of regulatory leadership has emerged. Australia's groundbreaking Cyber Security Act, which came into force in late May 2025, represents the world's first mandatory ransomware payment reporting regime. This legislative innovation, examined by the CNC Team this week, positions Australia to establish global standards for cyber transparency and threat intelligence sharing.
The Australian model offers a potential pathway for regional coordination that could fundamentally alter the cybercriminal calculus. By forcing transparency around ransomware payments and creating comprehensive threat intelligence databases, Australia demonstrates how legislative courage can transform national vulnerability into collective strength.
For a region fragmented by diverse regulatory frameworks and competing national interests, Australia's bold experiment provides a template for harmonized cybersecurity governance. The convergence of mandatory reporting requirements with the escalating regional threat landscape creates an unprecedented opportunity for intelligence gathering and coordinated response—if other nations possess the political will to follow Australia's lead.
The question now facing Asia-Pacific is whether other governments will embrace Australia's transparency revolution or continue allowing cybercriminals to exploit the region's digital divisions. The answer may determine whether Asia-Pacific remains cybercrime's promised land or becomes the birthplace of a new era of cyber resilience.
Sign up for Cyber News Centre
Stay one step ahead in cyber, AI, and tech news! Sign up now for exclusive alerts, expert analysis, and the latest breakthroughs—delivered straight to your inbox. Don’t miss out—join the CNC community today!
The AI-assisted raid on South Korea's banks never went near the vault. It slipped in through loan portals, sales platforms and a staff mobile app. Now Seoul is ordering every bank to count its exposed doors, and regulators in Washington, London, Frankfurt and Sydney are asking the same question.
OpenAI flew its chief strategy officer to Sydney to apologise for a rogue AI agent's Medicare breach. The hack was clumsy. The silence that followed was worse, and Parliament now has to decide whether sorry is the only accountability on offer.
Anthropic’s Fable 5 briefly gave Australia a rare look at Mythos-class cyber AI in action. Then US export controls shut access down, raising a harder question: if the model is too dangerous to leave America, are allies left safer, or simply more exposed?
Anthropic’s Mythos turns hacking from craft to industrial process, shifting power towards attackers just as Japan’s megabanks move to adopt it and Australian regulators warn banks and tax agencies to brace for AI‑speed cyber threats.
Where cybersecurity meets innovation, the CNC team delivers AI and tech breakthroughs for our digital future. We analyze incidents, data, and insights to keep you informed, secure, and ahead. Sign up for free!